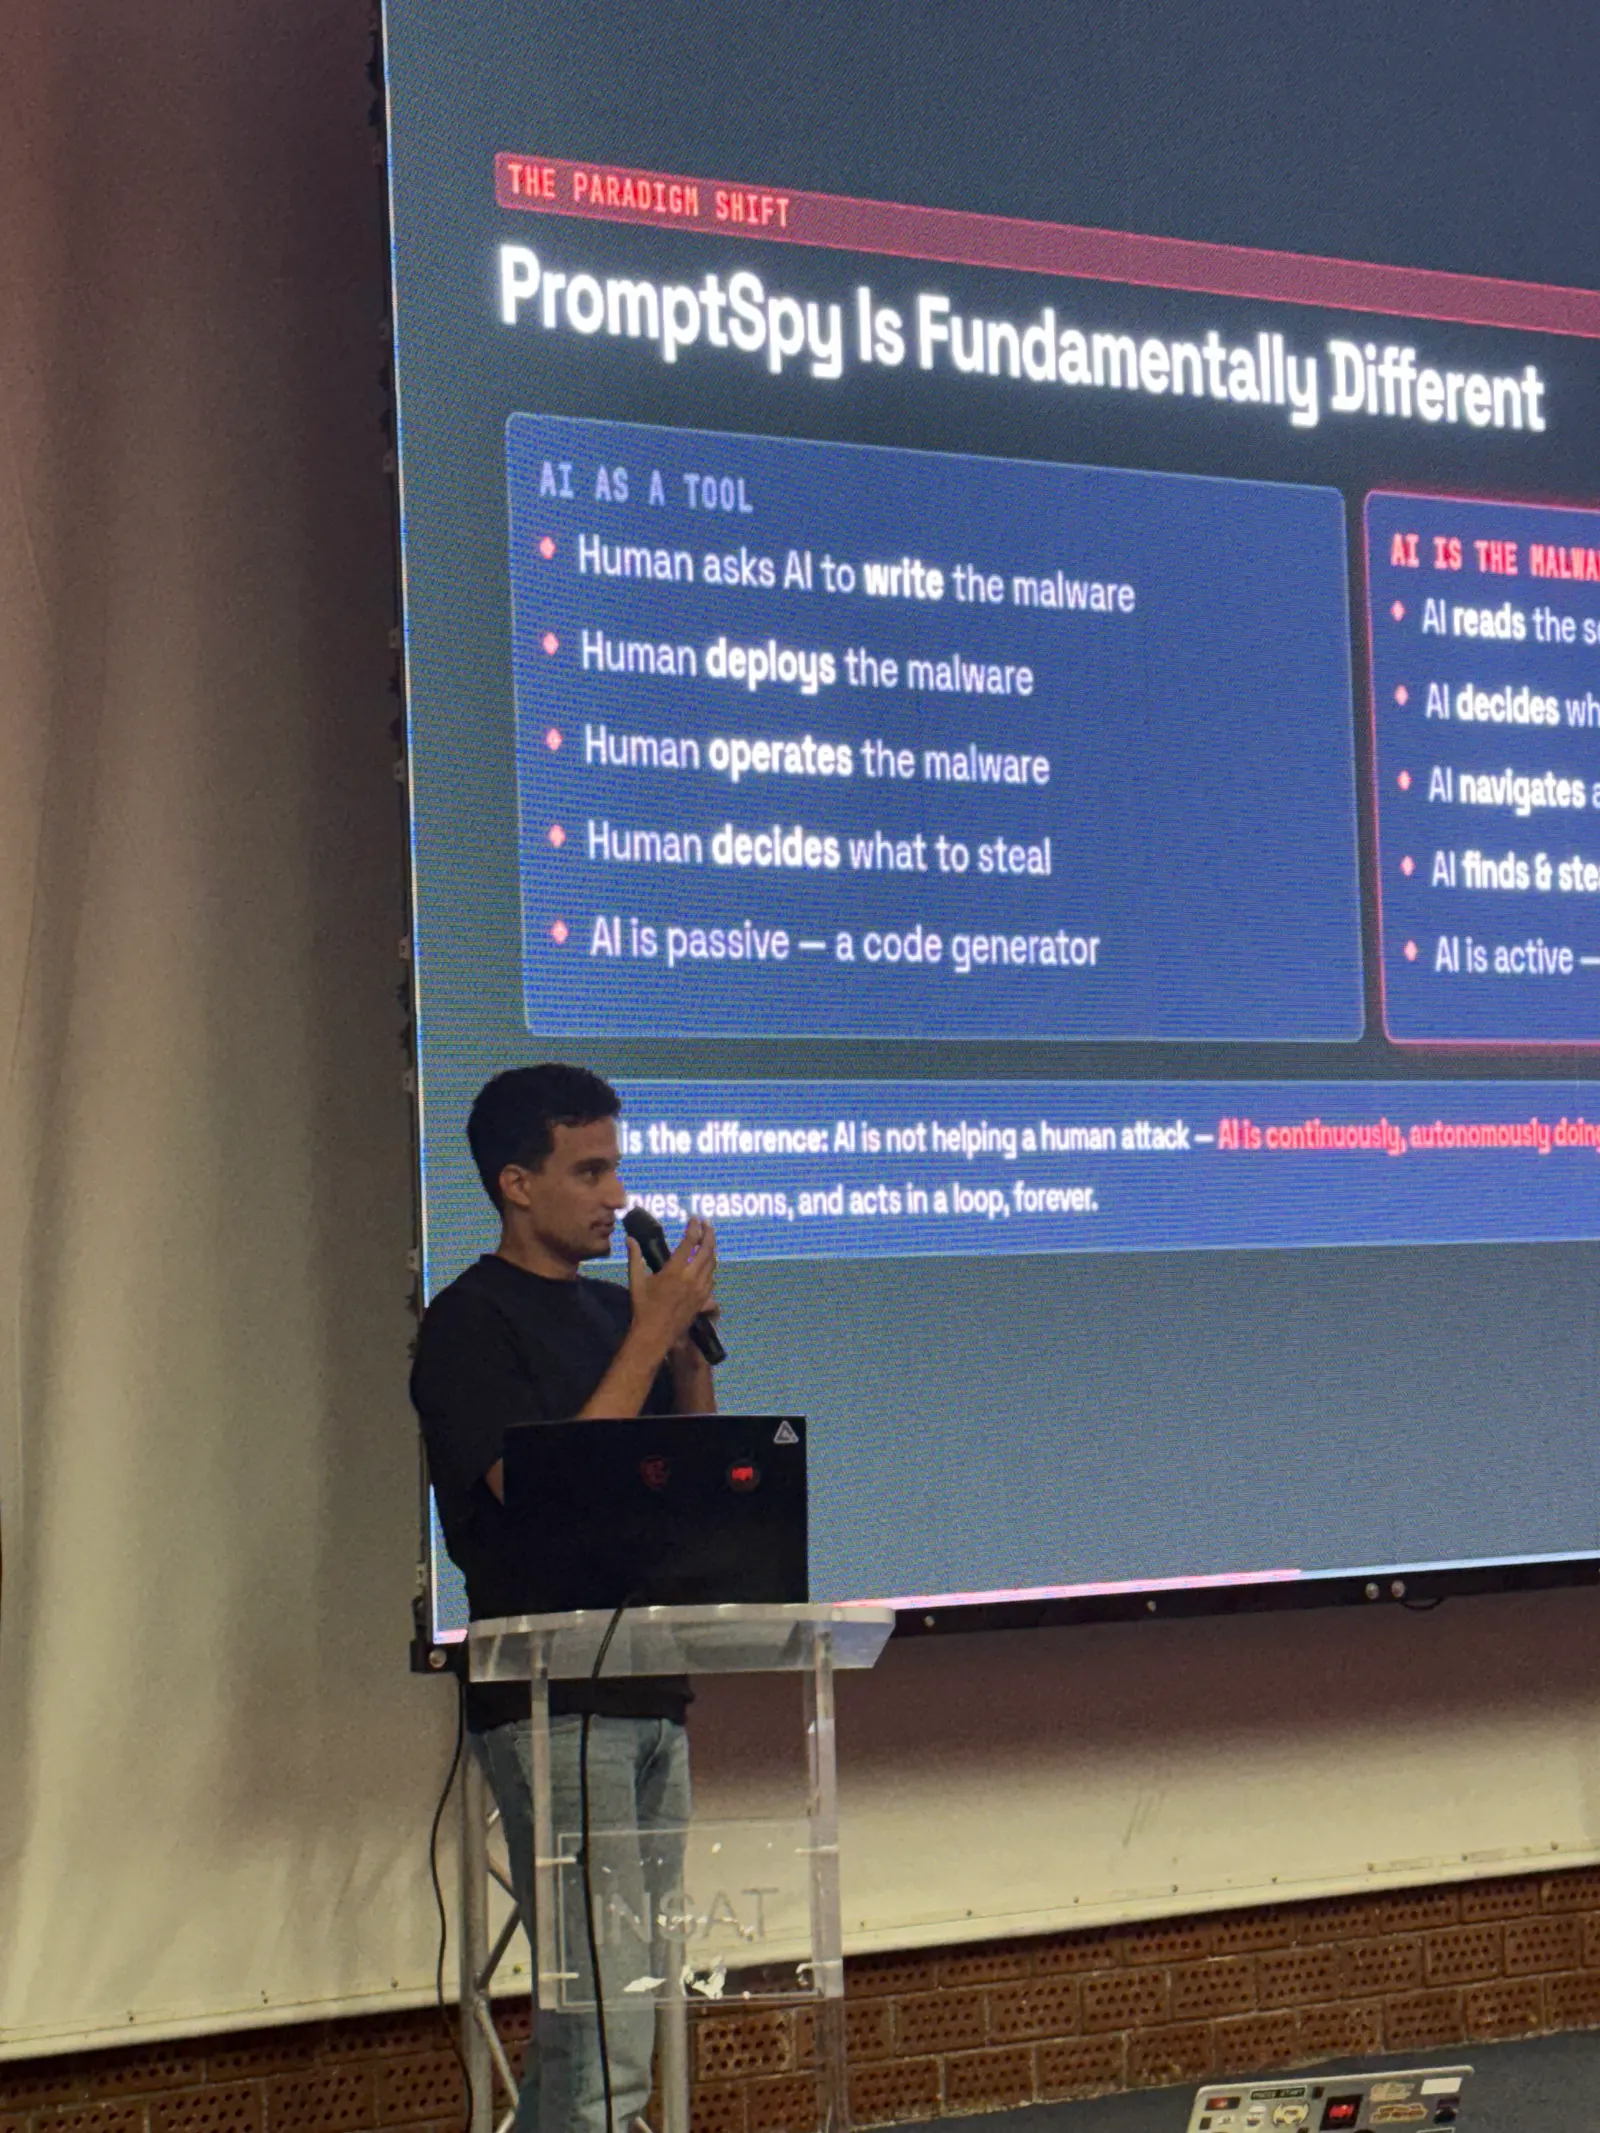
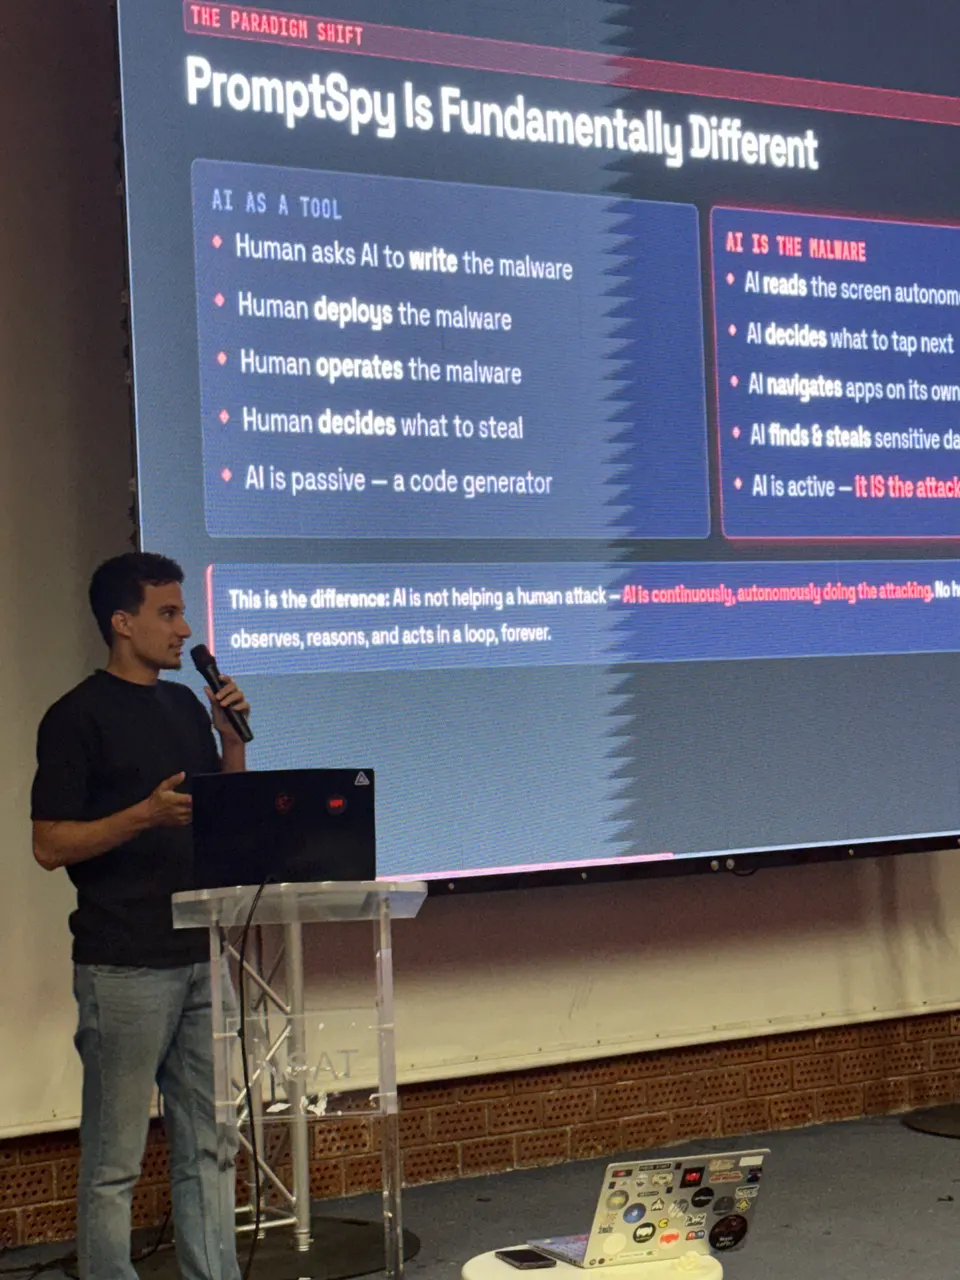
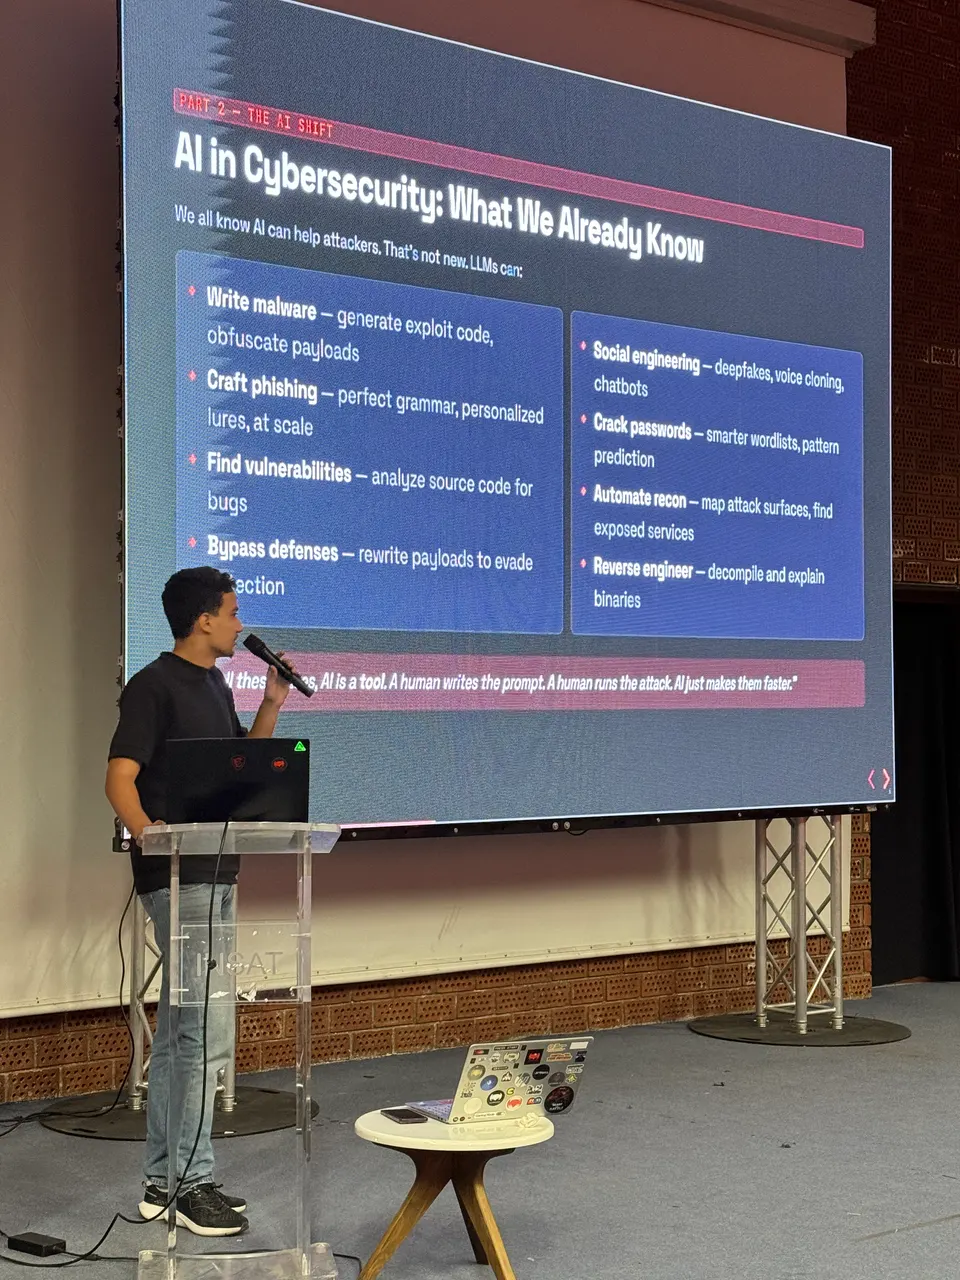
Khalil speaking at the lectern during a workshop on AI and cybersecurity.
00
Cybersecurity & engineering
Security through curiosity.
I’m an engineering student at INSAT specializing in Networks and Telecommunications, with a strong interest in cybersecurity. I enjoy exploring how systems work at a low level, especially through reverse engineering, binary analysis, and Android application reversing.
I’m an engineering student at INSAT specializing in Networks and Telecommunications, with a strong interest in cybersecurity. I enjoy exploring how systems work at a low level, especially through reverse engineering, binary analysis, and Android application reversing.
Competitions & challenge design
Outside of my studies, I regularly take part in CTF competitions, work on personal projects, and occasionally create challenges of my own. These experiences have helped me develop practical skills in areas like Android security, exploitation, and debugging.
Hands-on penetration testing
I’m currently sharpening my skills in system and web penetration testing through hands-on labs on dedicated learning platforms. My goal is to build a solid understanding of systems and security, and to create tools and solutions that are both useful and reliable.
AI workflows & automation
In parallel, I’ve been diving deeper into the effective use of AI — focusing on prompt engineering, workflow optimization, and the integration of tools such as MCP servers — to leverage AI as a practical, reliable component within security-focused workflows. I’m currently exploring the intersection of AI agents and offensive security automation.
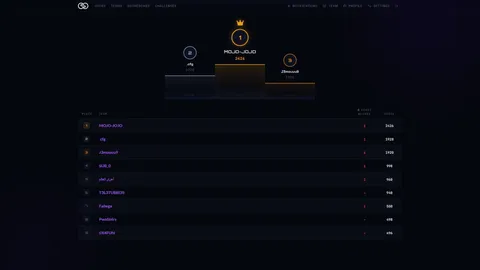
1st Place CTF, CyberCamp, Africa Top 4, World Top 7, Global Top 1%, World Top 8, Hackathon Top 4, 2nd Place, Challenge Author, +20 CTF Event Podium, Team MOJO-JOJO
1st Place CTF
CyberCamp
Africa Top 4
World Top 7
Global Top 1%
World Top 8
Hackathon Top 4
2nd Place
Challenge Author
+20 CTF Event Podium
Team MOJO-JOJO
1st Place CTF
CyberCamp
Africa Top 4
World Top 7
Global Top 1%
World Top 8
Hackathon Top 4
2nd Place
Challenge Author
+20 CTF Event Podium
Team MOJO-JOJO
Milestones01
Key Achievements
+0CTF Event Podium
Top 0%TryHackMe Worldwide
011st Place CTF
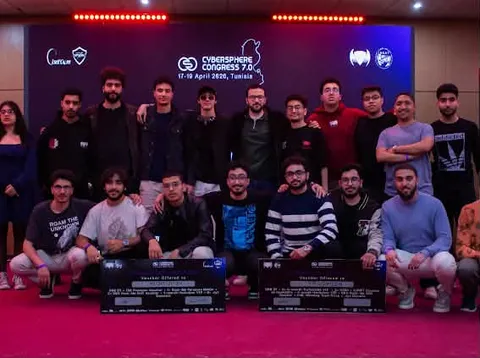
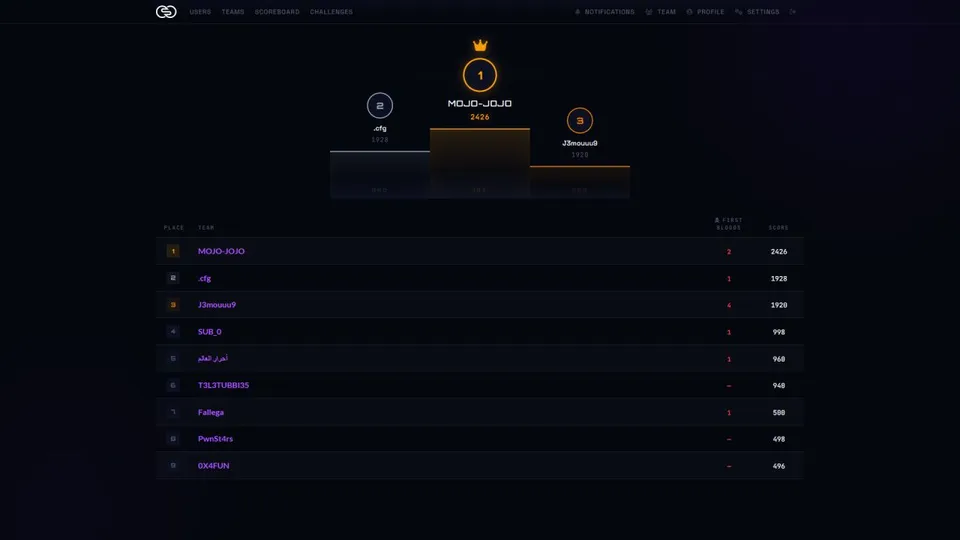
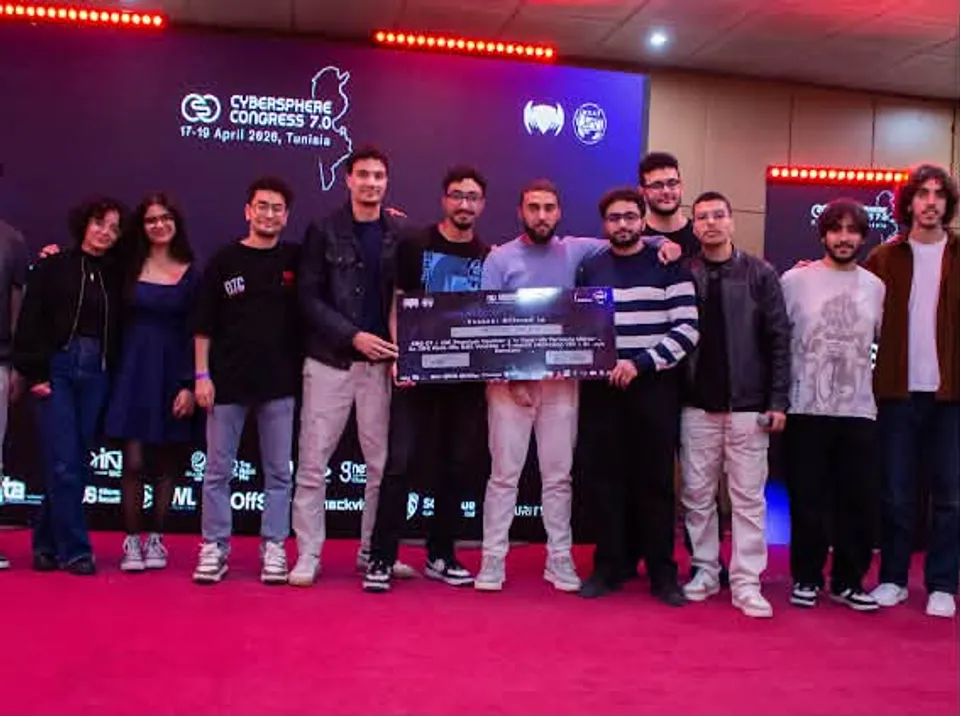
1st Place - Cybersphere Congress Advanced CTF
Organized by Securinets INSAT. Restricted AI use. Gained hands-on experience and overcame complex challenges. Prizes: 2x .xyz domains, INE premium voucher, Root me parcours metier, Root me gift cards.
02CyberCamp
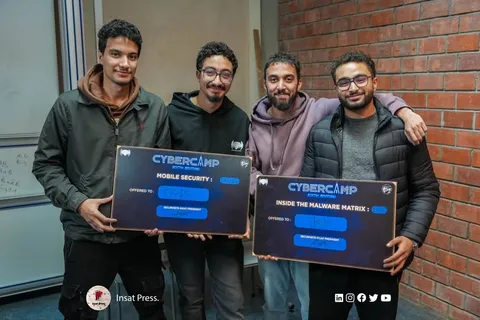
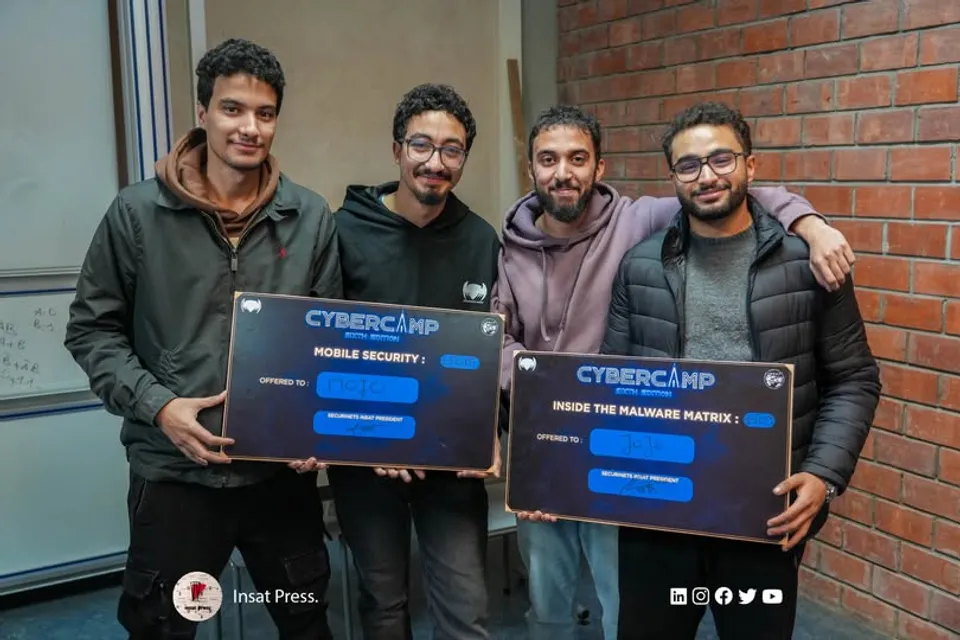
1st Place - CyberCamp Bootcamp & Competition
Winner in mobile penetration testing track.
03Africa Top 4
Top 4 in Africa - Securinets CTF Qualifiers
Strong offensive security performance at continental level.
04World Top 7
Top 7 Worldwide - Securinets International Finals
Ranked among the leading international teams.
05Global Top 1%
Top 1% - TryHackMe
Completed pentesting and SOC learning paths with practical labs.
06World Top 8
Top 8 Global - Cybears Algeria Qualifiers
Strong performance against international teams in the qualifiers.
07Hackathon Top 4
4th Place - Hack For Good Hackathon
Developed HANINY, an AI-powered driver monitoring system. Placed 4th out of 54 teams and pitched to over 500 people.
082nd Place
2nd Place - DarkNets CTF 3.0
Competed primarily in Reverse Engineering, while also tackling Web, Pwn, and Cryptography challenges.
09Challenge Author
CTF Author & Organizer - MOJO JOJO CTF
Hosted a Capture The Flag event, authoring and designing the Web Exploitation challenges.
Work02
Featured Projects
Project ArchitecturesPROJECT: 01 / 07
Honeypot
LLM-Powered Adaptive Honeypot
CowrieFastAPIWazuhDockerPython
Summary
Built a deception platform as a layered pipeline: Cowrie/FastAPI collect attacker input, a policy-gated LLM generates realistic responses, and Wazuh ingests normalized telemetry. The key value was not only trapping attackers longer, but learning how to turn noisy interaction logs into structured intelligence we could act on.
Core Features
Core Aspect
Dynamic LLM-driven SSH and HTTP interaction modules
Core Aspect
Policy-guided output sanitization and model gating
Core Aspect
Centralized event normalization and Wazuh SIEM integration
Core Aspect
Automated IoC extraction from adversarial sessions
Advanced certification focusing on managing and executing complex Red Team operations, including planning multi-phase adversary simulations, leading red team engagements, and aligning offensive scenarios with real-world threat intelligence.
Comprehensive certification covering the full spectrum of phishing attack methodologies, social engineering tactics, and organizational defenses. Covers email threat analysis, lure identification, user awareness program design, and technical countermeasures to protect against modern phishing campaigns.